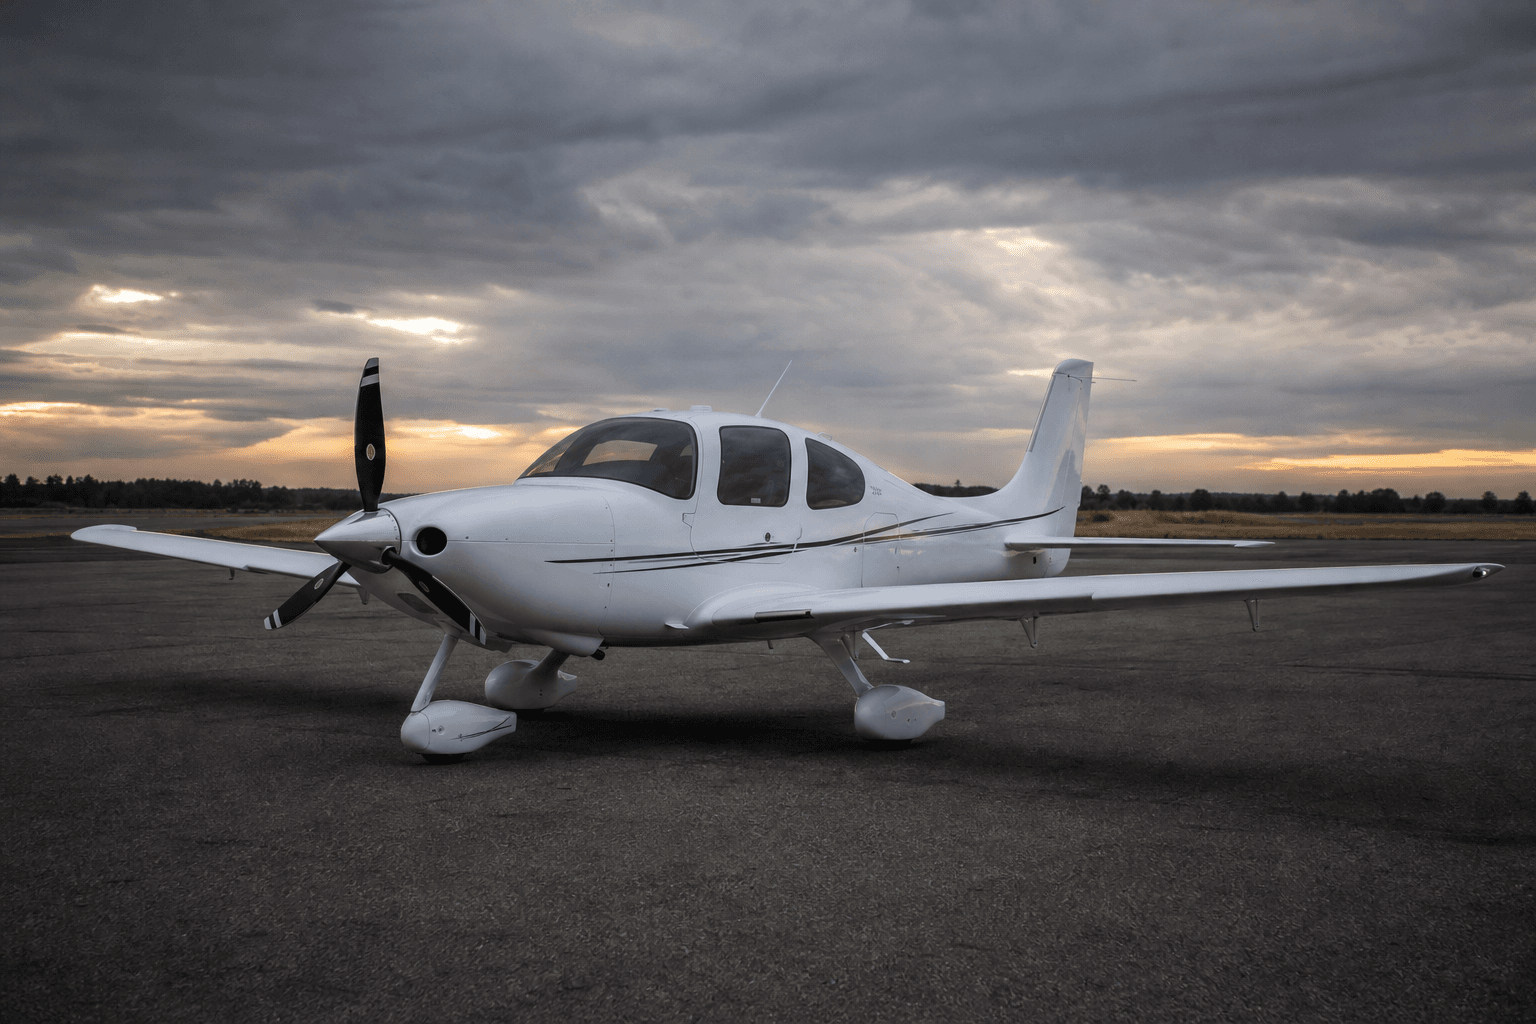
AI-generated illustration
Cirrus Data Breach Exposed Social Security, Medical and Passport Records for Nearly 3,900 People
Cirrus Aircraft says a July social engineering attack exposed financial, medical and government ID data, and it waited until November 10 to notify state attorneys general.
The gist
A July social engineering attack on Cirrus exposed SSNs, bank and card numbers, medical data and passport details for about 3,903 people.
Cirrus Aircraft has disclosed a data breach that exposed Social Security numbers, bank and credit card details, medical information and government identification records belonging to roughly 3,903 people. The Minnesota-based maker of the SR-series piston singles and the Vision Jet said the breach took place on July 17. The company described it as a sophisticated social engineering incident that led to sensitive information being disclosed to an unknown party.
Cirrus has not said publicly how many people were affected. The 3,903 figure comes from the company's notification to the Texas attorney general, which was cited by Dapeer Law Firm and data security firm Black Shard. That filing states that 280 of the affected individuals live in Texas. Public documents show another four live in Vermont, and the number of affected Massachusetts residents has not been disclosed.
The list of exposed data is long. According to the state filings, it includes names, addresses, login credentials, Social Security numbers and medical information. Financial records such as credit card numbers and bank account numbers were also compromised. So were government identification numbers, including driver's licenses, passports and state ID cards.
A Cirrus spokesperson said the company identified the incident, moved immediately to address it and opened an investigation into the nature and scope of the activity. The company brought in outside cybersecurity forensic specialists to help with that work. Cirrus formally notified state attorneys general on November 10, close to four months after the breach occurred.
The company has not said whose records were taken. It has not specified whether the victims are aircraft owners, prospective buyers, employees or contractors. The size of the affected group is close to the company's recent delivery count: General Aviation Manufacturers Association shipment reports show Cirrus delivered 4,218 aircraft between 2020 and the first half of 2026. The match is approximate, and Cirrus has not linked the two figures.
Cirrus is offering affected individuals a free 24-month membership with Epiq credit monitoring across all three major credit bureaus. The service includes alerts for new credit inquiries, new accounts and public records. People can enroll with the activation code printed in their notification letter from Cirrus. Epiq can be reached at 866-675-2006 for questions or for help placing a credit freeze.
The Federal Trade Commission advises anyone whose data has been compromised to check, freeze and monitor their credit reports right away. Each of the credit reporting agencies offers free accounts that let consumers carry out those steps. Cirrus has also set up a dedicated toll-free call center for questions about the incident at 888-650-4420. It is staffed Monday through Friday from 9 a.m. to 9 p.m. Eastern time.
Originally reported by AOPA
Read more
All General Aviation →
Airbus Eager to Launch A320neo Successor as Boeing Says Market Is Not Ready for a New Narrowbody
At a UK aerospace conference, Airbus said airlines want its Next-Generation Single-Aisle now, while Boeing said demand for a 737 Max replacement has cooled since last year.
Air India Drops Rome Fuel Stops and Restores Non-Stop Delhi and Mumbai Flights to New York and Newark
With airspace restrictions easing, Air India is again flying all four of its India to New York-area routes without technical stops, cutting journeys from about 22 hours to roughly 17.
FAA Lets BETA Fly Prospective Customers Aboard ALIA A250 eVTOL Ahead of Certification
A special airworthiness certificate for market survey operations allows BETA Technologies to carry potential operators on A250 demonstration flights, though commercial passenger service remains off limits.
Burbank Tower Goes ATC Zero Twice in One Evening, Leaving Airline Crews to Self-Announce on CTAF
Southwest and Alaska Airlines pilots at Hollywood Burbank Airport coordinated their own movements on a common frequency during roughly 30-minute gaps with no controller in the tower.
The Daily Touch & Go
The day's best aviation news in your inbox. Free, no spam.